
On July 2, 2026, the FBI and Google's Threat Intelligence Group executed a coordinated operation against NetNut, one of the largest commercial residential proxy networks in the world.
Customers who relied on NetNut for data collection, account management, or market research woke up to service interruptions. Domains were seized. Connections failed. Support went silent.
If you are one of those users, you are not alone. And you do not have to wait for a service that may never return.
What Actually Happened to NetNut?
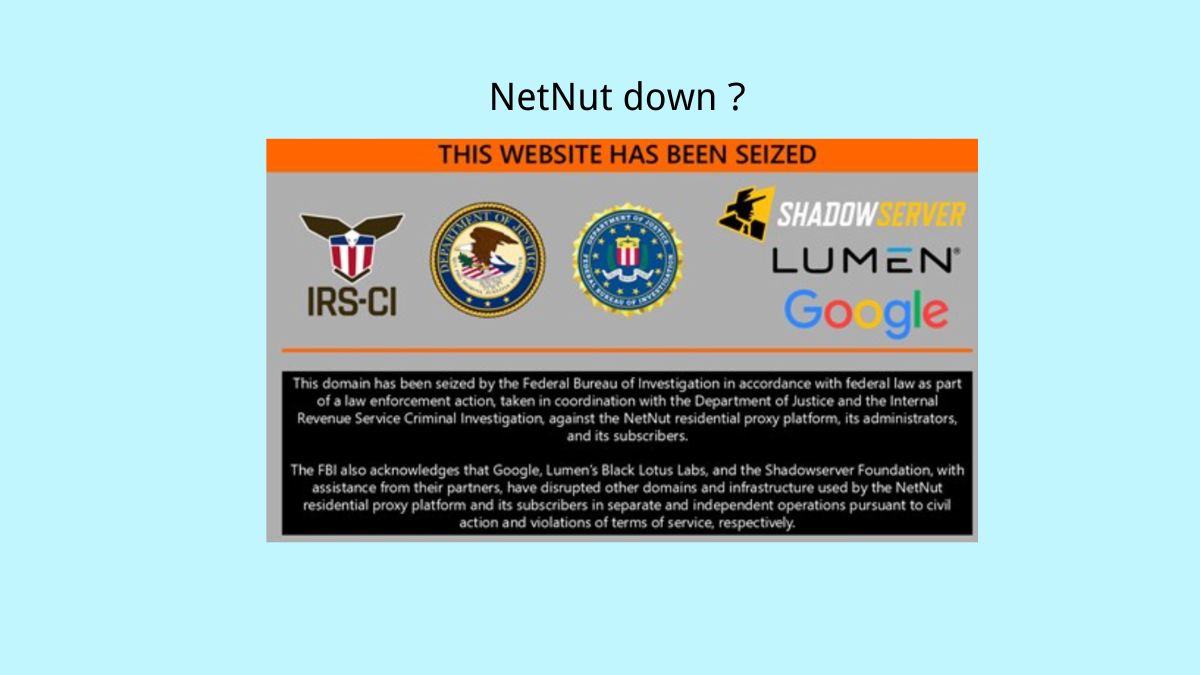
The enforcement action was not a simple website takedown. It was a large-scale international operation targeting NetNut's entire infrastructure.
The FBI seized hundreds of domains associated with the service. Google deployed immediate technical mitigations alongside the legal actions, including disabling all Google accounts used by NetNut for malware command-and-control and updating Google Play Protect to automatically block affected applications.
Industry partners including Lumen Technologies, the Shadowserver Foundation, and the US Internal Revenue Service's Criminal Investigation division all participated in the operation.
NetNut's parent company, Alarum Technologies Ltd, a publicly traded Israeli firm listed on NASDAQ, confirmed the domain seizures. The company stated it would "fully cooperate with law enforcement to ensure any misuse of its infrastructure is thoroughly investigated and those responsible are held to account".
However, Alarum has not announced a formal closure or liquidation of NetNut. For customers, this creates immediate operational uncertainty. A company may remain registered while its gateways, IP supply, or customer workflows stop working.
Why Was NetNut Targeted?
The investigation centered on NetNut's connection to a botnet called Popa.
At the heart of the NetNut residential proxy service was the Popa botnet, an engineered stealth communications layer. By embedding deceptive software development kits into inexpensive Android-based smart TVs, streaming media boxes, and unofficial apps like the SmartTube client, NetNut hijacked ordinary home electronics.
When consumers plugged in these devices, their home internet connections were quietly rented out as residential proxy exit nodes. This allowed malicious traffic to route through legitimate domestic IP addresses, effectively bypassing standard data center blocks and security filters.
The Scale Was Massive
| Finding | Detail |
|---|---|
| Devices co-opted | Over 2 million consumer devices globally |
| Software variants | Approximately 5,000 variants of the Popa architecture |
| Control infrastructure | 46 controller domains and more than 300 backend servers |
| Threat actors using the network | At least 316 distinct threat clusters in a single week |
| Activities enabled | Password spraying, credential stuffing, advertising fraud, sensitive data scraping |
While Alarum historically marketed its software as a consensual bandwidth-sharing tool, independent technical reviews found that hijacked host applications failed to present users with any clear notice or consent prompt. Researchers recorded 10 million proxy requests and reported that most tested apps did not present meaningful consent notices.
Independent cybersecurity journalist Brian Krebs reported that NetNut could be linked to Alarum Technologies Ltd. Security firms Qurium and Synthient both established direct links between Alarum's executive leadership and the original developers of the malicious Popa software development kit.
The Whitelabel Problem Is Bigger Than NetNut
Google's report highlighted a broader issue. NetNut has "a robust reseller program that allows whitelabeling of its network". The company assessed with "high confidence" that many popular residential proxy brands are in fact whitelabeling the NetNut botnet.
In plain terms: they are reselling access to a network of hijacked devices under their own brand name, and their customers have no idea.
This is how parts of the residential proxy industry actually works. When a provider's own botnet gets degraded, whether from a law enforcement takedown, ISP blocking, or just devices going offline, they buy capacity from other botnets and keep selling. The whole ecosystem is tangled together.
What this means for businesses buying residential proxies is simple: the brand name on your dashboard might have nothing to do with where your traffic is actually going.
Why Proxy Buyers Should Care
If you are using residential proxies for web scraping, ad verification, market research, or competitive intelligence, here is why this matters to you directly.
You might have legal exposure. When your traffic routes through devices that were enrolled without the owner's consent, you are part of a chain that starts with unauthorized access to consumer hardware. "I did not know my provider was using malware-infected smart TVs" is not a strong legal defense.
Your infrastructure is fragile. Botnet-sourced networks are unstable by nature. Google just proved, for the second time in six months, that it can degrade these networks at scale. If your business depends on residential proxy access, you do not want to be building on top of a botnet.
Your IPs carry baggage. Google's report directly links residential proxy botnets to espionage groups, DDoS infrastructure, and credential stuffing campaigns. If your provider's network overlaps with theirs, the IP addresses you are using have that history attached. That means higher block rates, more CAPTCHAs, and the risk of showing up in threat intelligence databases alongside actual threat actors.
How to Choose a Proxy Provider You Can Trust
The NetNut takedown is a reminder. Low prices and large IP pools are not enough. You need to know where those IPs come from.
Here is what to look for in a reliable residential proxy provider:
1. Transparent IP sourcing. The provider should clearly explain how they acquire their IPs.
2. Consent-based networks. All devices in the pool should be enrolled with informed user consent. Real consent means more than a buried clause in an app's terms of service.
3. Own infrastructure. Google's report makes it clear that whitelabeling is everywhere. If your provider cannot tell you exactly where your traffic is routing, there is a good chance they do not know either.
4. Clean compliance record. No history of enforcement actions or legal disputes.
5. Stable service. Consistent uptime, reliable support, and clear communication.
Why UnoProxy Is the Smart Choice
UnoProxy takes a different approach. We believe that reliable proxy service should never come at the cost of ethics or compliance.
Clean, consent-based IP sourcing
All Unoproxy residential IPs come from legitimate telecom carriers and ISPs. Every device in our network is enrolled with proper user consent. No hidden SDKs. No compromised smart TVs. No botnets.
Stable, high-performance infrastructure
Our network delivers consistent connection success rates above 99.5% with average latency under 100ms. You get the performance you need without the uncertainty.
Global coverage
We cover over 50 countries with residential and mobile IP options. Whether you need US, European, or Asian IPs, we have you covered.
Enterprise-grade compliance
We enforce a strict zero-tolerance policy against misuse. Our infrastructure stays clean, transparent, and safe from the kind of legal actions that took down NetNut.
Dedicated support
When you have questions, you get answers. Our support team responds quickly and actually solves problems.
Thousands of cross-border sellers, e-commerce operators, and data teams already trust Unoproxy. They rely on us for stable, ethical proxy service that keeps their operations running smoothly.
What to Do Right Now
If you were using NetNut and need a replacement:
- Audit your current integrations. Document which workflows depend on proxies.
- Preserve your account records. Keep any relevant data from your NetNut account.
- Test a reliable alternative. Do not wait for NetNut to come back. The uncertainty is not worth it.
Final Thoughts
The NetNut takedown is not an isolated incident. The IPIDEA takedown in January and today's NetNut operation are part of a pattern. Google has made it clear that more disruptions are coming.
Law enforcement is increasingly focused on residential proxy networks that operate without proper consent. Providers who cut corners on compliance are playing with fire.
Your business should not be caught in the crossfire.
Choose a proxy provider that values transparency, ethics, and stability. Choose UnoProxy.
Switch now. Keep your operations running.
